

 Get Started
 Tutorials
 Expert Reviews


Not enough
Trust
A promise asks you to believe.
Security should not rest on belief alone. It should come with evidence you can check.
We open our work so customers, developers, and independent researchers can inspect it, question it, and help us make it better.
Read our open-source philosophyTechnical depth when you want it. Clear evidence when you need it.
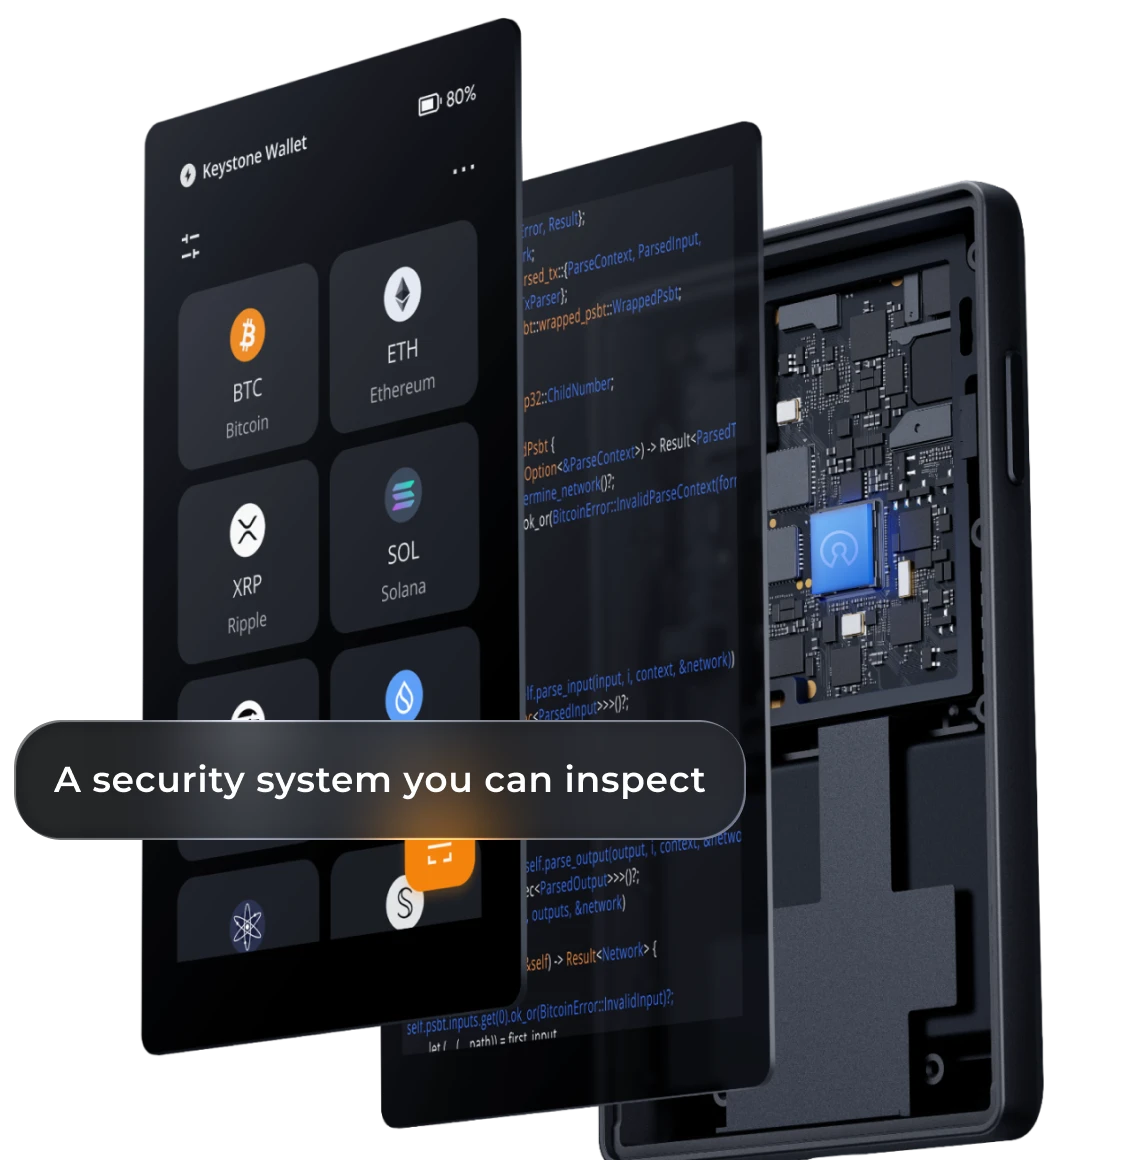
See how the wallet works.

Inspect schematics and the BOM.

Review evidence beyond Keystone.

Build from public source, compare the checksum, and check what runs on your Keystone.
View source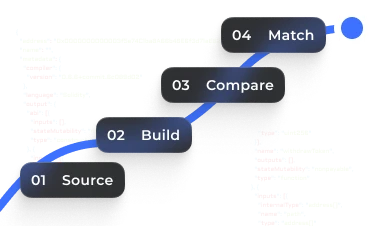
External scrutiny
It makes more of the system inspectable—and gives more people a way to find, report, and help improve weaknesses.
PRECISE, NOT ABSOLUTE
Keystone publishes the firmware and hardware materials it controls. Some third-party MCU libraries remain subject to vendor restrictions.

Your cart is currently empty.